MultiCloud Administrator
Administration of infrastructure spread across three cloud providers.
I correlate SIEM alerts, system and network logs, forensic findings, IOCs pulled from threat hunting and cyber intelligence context. Crossing those sources is what turns a lone alert into an investigation with a name, a scope and a response that holds up.
200 days: the global average time to detect a security breach.
I am Dario González Blanco, a cybersecurity specialist and systems administrator. I came to security after falling for a phishing attack in 2022, and since then I have worked so it does not happen to anyone else: from a systems and networking foundation to a master's in cyber intelligence.
Curious how I got here?
Read my story
Additional training, with verification where available.
CompTIA Security+ (SY0-701)
Blue Team Level 1 (BTL1)
eJPT — Junior Penetration Tester
Certificate of Proficiency in English (CPE) — Level C2
Swipe to browse · tap to open one
Where I have worked and where I have trained, kept apart.
Professional experience
Administration of infrastructure spread across three cloud providers.
Hands-on practice
Simulated real-world cases end to end, from alert to report.
Real vulnerable machines, compromised end to end.
Where the foundations come from.
Threat intelligence and APT group analysis.
Systems, network and virtualisation administration.
Alerts closed, investigations opened and machines compromised in the lab. What has actually been done, counted rather than described.
A sample of what I have been working on.
ASIR final project · 2025
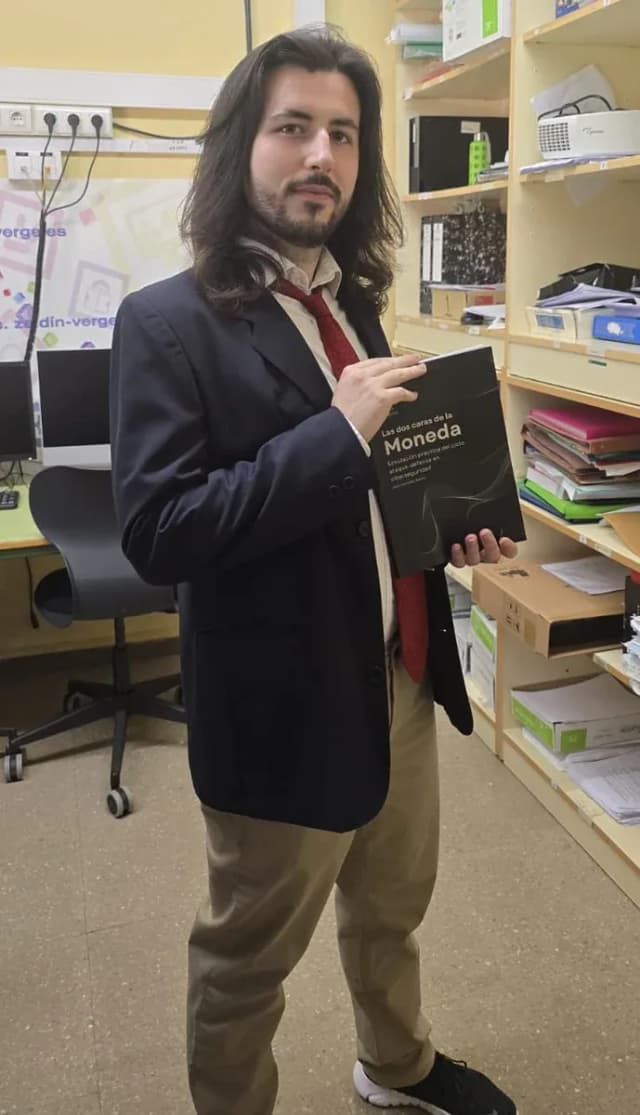
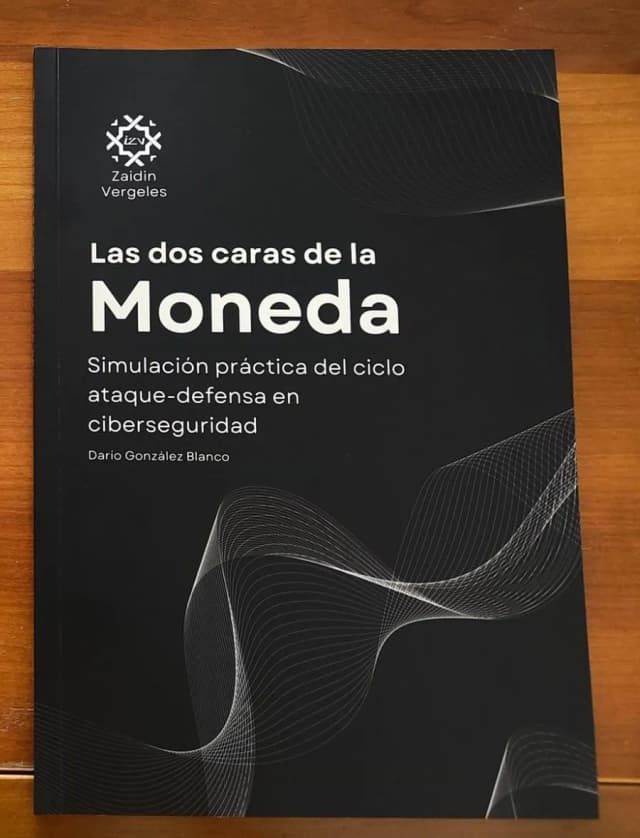
Published book on the attack-defence cycle in cybersecurity, with hands-on simulations of both sides.
Master's thesis · 2026
Full study of the Lazarus APT group: motivations, capabilities, infrastructure and behavioural patterns.
Design and development · 2026
Web tool that analyses suspicious emails and explains, step by step, why they are suspicious.
View projectHow I work
I use these tools at an advanced level, as an accelerator rather than a replacement for judgement. And so that privacy is not lost along the way, anything sensitive stays in house: I run local models with Ollama, one per task, so no data from an analysis ever leaves my machine.
 ChatGPT